ABOUT BYOC.MD
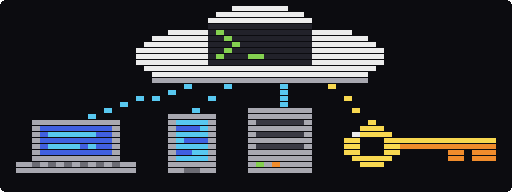
BYOC.md is a working idea: a plain markdown file for AI agents that work inside your own cloud account, with your own devices and keys, instead of a vendor's. It says where an agent may work, which devices it may reach, and which keys it may use. Keys are listed by name, never by value; the secret stays in your vault. The file states the limits; your cloud's own permissions enforce them.
WHAT IT COULD COVER
- the cloud: which accounts and regions, who pays, a monthly cap
- devices: which machines the agent may reach, and how it connects
- keys: each one by name and scope, where it lives, when it expires
- data: where it is stored, and what may leave your account
- the exit: how access is revoked, keys rotated and copies deleted
A SKETCH
---
byoc: draft
---
# BYOC.md
- cloud: our account, EU regions only
- monthly_cap: 300 USD, alert at 80 %
- devices: build server, office file server
- keys: by name from our vault, 1-hour expiry
- data: stays in our account
- exit: revoke access, rotate keys
- never: secrets in chat, logs or this file
DISCLAIMER
BYOC.md does not host, run or hold anything, and it does not grant or enforce access. It is no substitute for a security review. Keep passwords, keys and tokens out of the file and out of chats.
BYOC.md is an informational page. It is provided as is, without warranty of any kind, and may be incomplete, inaccurate or out of date. Nothing here is financial, investment, legal, tax or other professional advice, or an offer or solicitation. The sketch is an illustration, not a standard or a recommendation. Names of third-party products or companies, if any, are used only to describe them; no affiliation or endorsement is implied. Use at your own risk. This page sets no cookies and runs no scripts or analytics; like any website, its host keeps standard request logs.